FathomWatch
The problem
Malware is quietly stealing your people's passwords
Infostealer malware copies everything saved in a browser on an infected device, and the stolen logs are traded on the dark web, often long before anyone notices.
- Saved passwords
- Session cookies
- Card details
FathomWatch watches those logs for the domains your organization has verified and the email addresses you choose, and tells you when one of your people turns up.
How it works
From stolen log to resolved exposure
- Step 1
Add detectors
An org admin picks the organization's verified domains to monitor. Custom keyword or regex detectors, such as a brand name, are reviewed by our team before they go live.
- Step 2
We match the data
Each incoming log is checked against every active detector. You receive only the lines your detectors matched, never the rest of a log.
- Step 3
You get an exposure
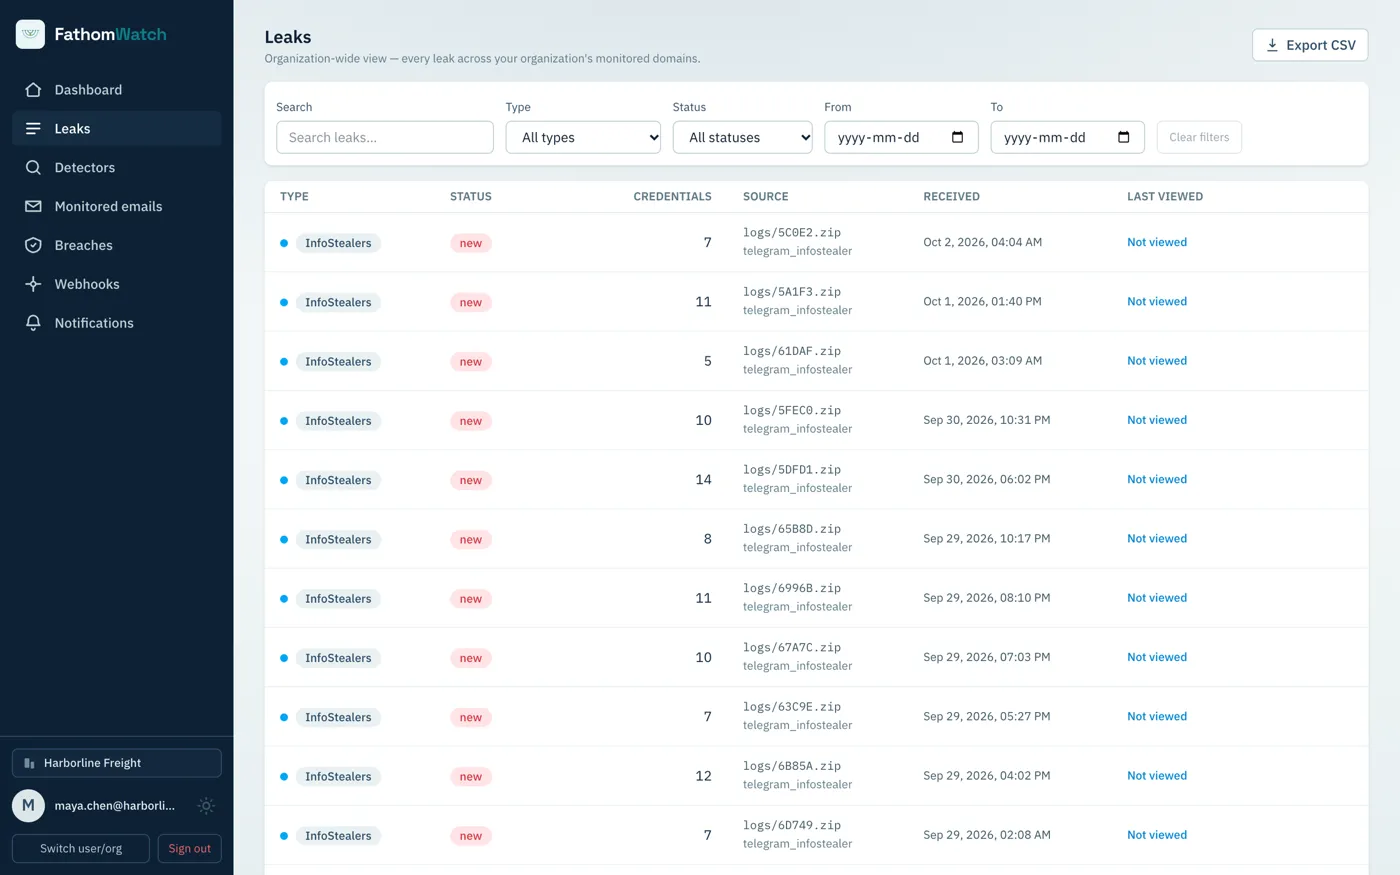
Each exposure shows the affected account, the sites whose logins were stolen, and a masked password. A credential that resurfaces later isn't reported twice.
- Step 4
Your team acts on it
Exposures move from new to investigating to resolved or dismissed, with notes everyone in the organization can see.
Help for the person affected
A recovery guide for every affected employee
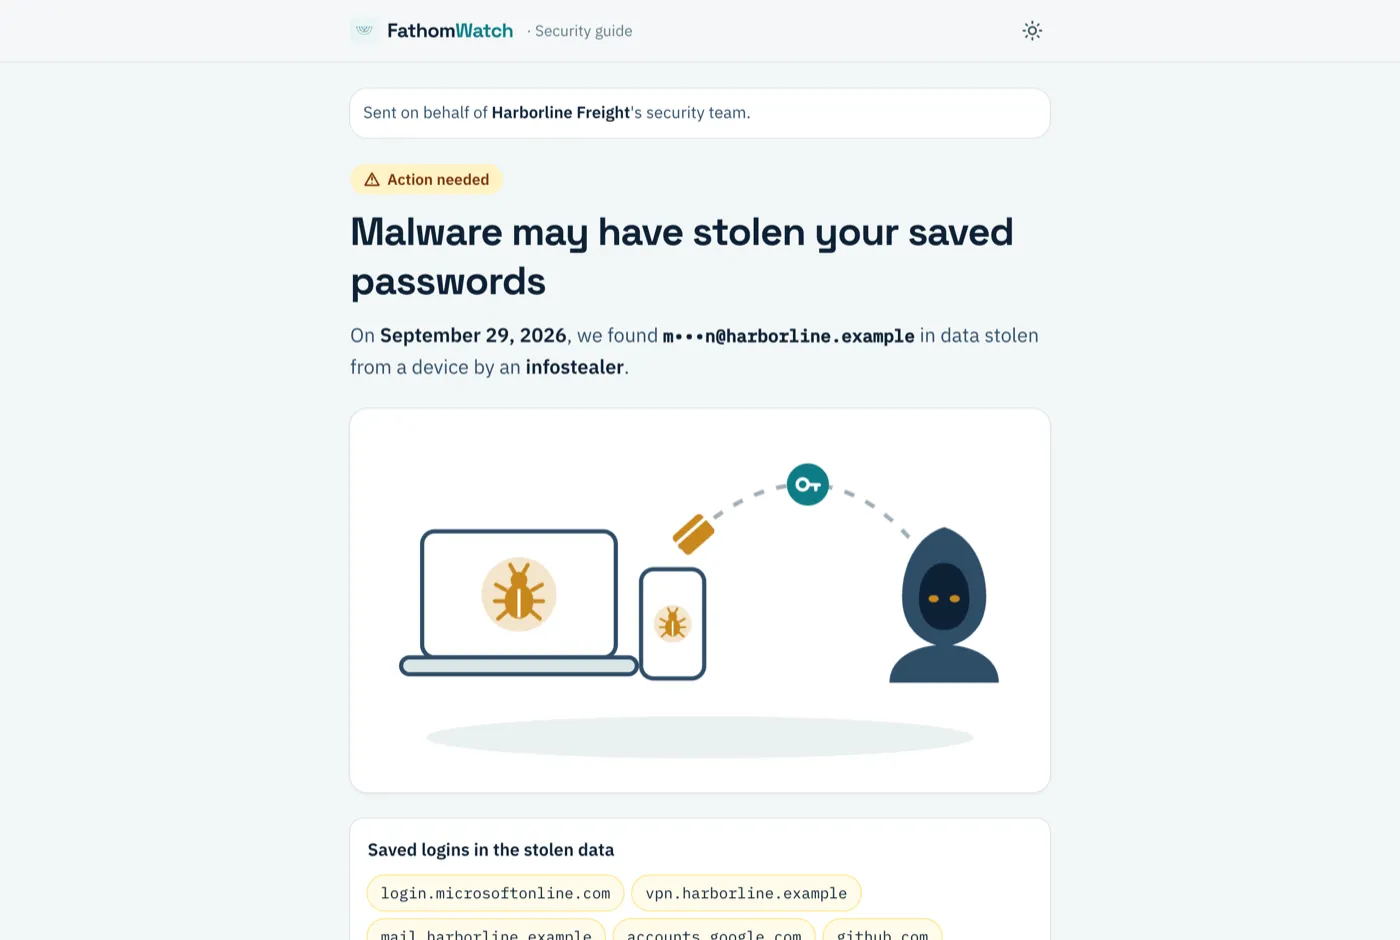
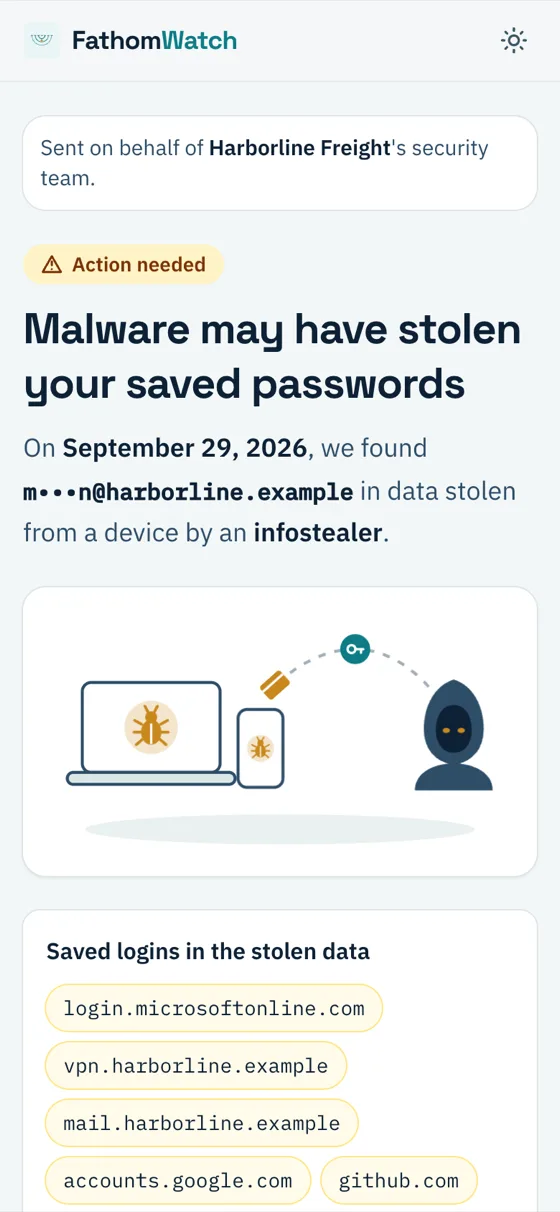
When an employee's work address is found in infostealer data, FathomWatch can email them a link to a step-by-step recovery guide.
- Sent on your organization's behalf, with your name and logo
- Explains what happened and which sites were affected
- Walks them through cleaning the infected device and securing their accounts, in the right order
- Never contains a password, and the guide needs no sign-in
Pricing
Priced by the size of your organization
One plan covers your whole organization, with no seats to assign. Billed monthly; add or remove users any time.
- 1–25 usersCA$39per month
- 26–100 usersCA$99per month
- 101–250 usersCA$179per month
- 251–500 usersCA$299per month
- 501–5,000 usersCA$499per month
More than 5,000 users? Contact us for a quote.
Personal plan: one person can monitor up to five of their own verified email addresses.
FAQ
Questions, answered
Everything teams usually ask before they start monitoring.
What does FathomWatch monitor today?
Infostealer logs: credentials stolen from infected devices. Combolists, credential leaks, database dumps, social media and dark web pages are being moved over from our previous platform.
Does FathomWatch store our passwords?
No. For each stolen credential FathomWatch keeps the account, the site, and only the first few characters of the password so its owner can recognise it. The full password is never stored or shown.
Do we see data about other organizations' people?
No. A stolen log can hold data about many people. Your organization receives only the lines your own detectors matched.
What do we need to set up?
An org admin chooses which of your organization's verified domains to monitor. You can also request custom keyword or regex detectors, such as a brand name, which our team reviews before they go live. With a Personal plan, individuals can add up to five of their own email addresses, each confirmed with a code.
Who in our organization sees the exposures?
Org admins, and members of any group you map to the Security analyst role, see every exposure in the organization. Everyone else sees only exposures of their own address. Exposures of someone's personal addresses are visible only to them.
Are employees told when their details are found?
People who use FathomWatch are always emailed about their own addresses. Org admins can also turn on emails for everyone else under your monitored domains. The email links to a step-by-step recovery guide sent on your organization's behalf; it never contains a password, and the guide needs no sign-in.
How do exposures reach our other tools?
Through webhooks (signed JSON sent when a new exposure arrives, a status changes or a known credential resurfaces), scheduled email digests with a CSV attached, and CSV export from the leak inbox. These are part of the Organization plan.
What happens if our subscription ends?
The account owner is emailed, and your detectors keep working for 7 more days. After that, monitoring pauses and a second email confirms it. Your detectors and existing results are kept, and monitoring resumes automatically when you renew.