OrbitalCyber
Every vulnerability in one place: endpoints, networks, your internet edge, cloud accounts, container images and code
All your vulnerabilities in one place, tracked until they’re fixed
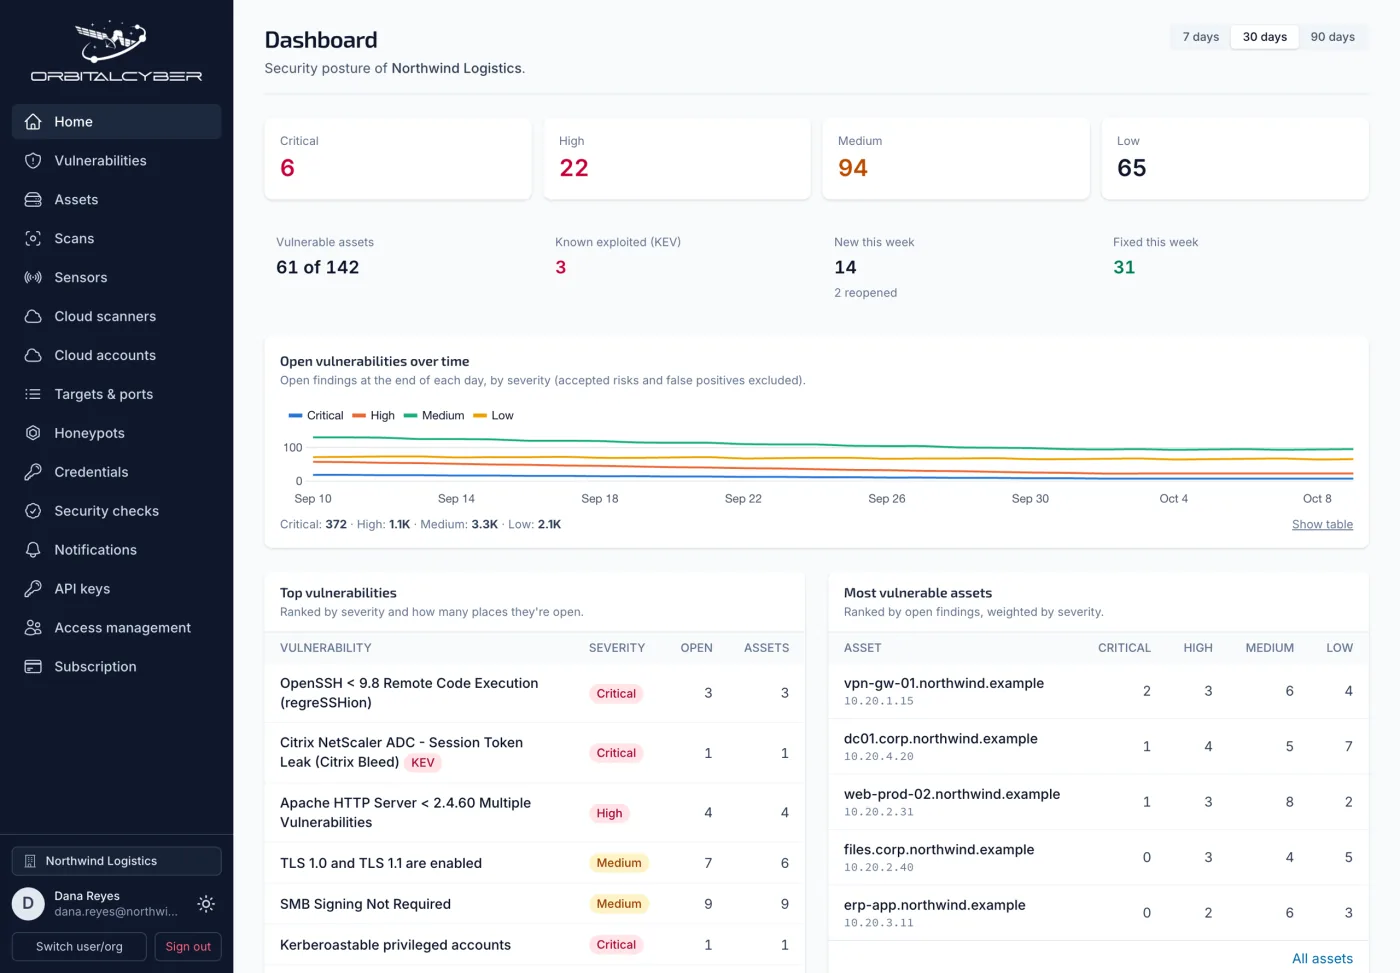
OrbitalCyber brings vulnerabilities from your endpoints, networks, internet edge, cloud accounts, container images and code repositories into one console. Scans run from sensors you install on your own networks or from cloud scanners we operate, endpoint agents report what’s installed on your computers, honeypots catch intruders, and every finding is tracked on the asset it was found on until a later scan shows it’s gone.
Features
Scans from your own sensors
Install a sensor on your network and scan whatever it can reach. Scans from your own sensors aren't metered.
Sensors and cloud scanners
Scan inside your networks from sensors you install, and your internet edge from our cloud scanners — one console for both.
Scan windows and blackouts
Keep scans to the hours you allow, with blackout dates for change freezes. Scans pause at closing time and resume where they left off.
Vulnerabilities tracked to the fix
Findings are tracked per asset, known-exploited ones are flagged, and a finding closes as fixed when a later scan no longer sees it.
Fixes ranked by impact
Top fixes group findings by the action that resolves them, so the fewest changes close the most findings.
TLS/SSL grading
Every TLS endpoint graded, with protocols, ciphers, certificate checks and real Heartbleed and CRIME probes.
AD attack paths, certificate services and GPO audit
BloodHound, PlumHound, Certipy, NetExec and a Group Policy audit run on your sensor; the domain data never leaves it.
AWS, Azure, Google Cloud and Microsoft 365 compliance
Prowler checks for AWS, Azure, Google Cloud and Microsoft 365, with compliance per framework and tracked findings per account.
Honeypots that alert
Decoy services on idle sensors record attackers' logins and commands, with email digests and signed webhooks.
Credentials kept secret
Scan credentials are encrypted at rest and decrypted only in the memory of the sensor running the scan.
Endpoint agents
Windows, macOS and Linux computers report their installed software and updates, so you see vulnerabilities on laptops that network scans can’t reach.
Container image scanning
Public and private images checked for vulnerable packages, end-of-life base images, leaked secrets and risky configuration, with tracked repositories.
Code scanning (beta)
Git repositories scanned on your own sensors for code flaws, vulnerable dependencies, secrets and infrastructure-as-code problems. Your code never leaves your network.
Known-exploited flags
CISA’s Known Exploited Vulnerabilities catalog is checked every 12 hours, and matching findings are flagged straight away, without a new scan.
Plans start at CA$12 per month, and every business plan comes with a 30-day free trial.
Choose from Home, Starter, Professional, Business and Scale plans. Scans from your own sensors are never metered, and on Starter and higher plans, cloud scans use the credits included with your plan each month. Having a penetration test with Sage ISG? One year of OrbitalCyber Starter is included with every test.
View Plans & Pricing