NullWard
Why it matters
Why your web applications need a firewall
Your websites, customer portals and APIs are open to the whole internet, and attackers probe them constantly with automated tools. A network firewall lets that traffic straight through because it looks like ordinary web requests. A web application firewall inspects every request and stops the attacks hidden inside before they reach your code.
Standards are catching up too: PCI DSS v4.0 requires public-facing web applications to be protected by an automated solution that detects and prevents web-based attacks.
Injection attacks
SQL and command injection slip malicious instructions into forms and URLs to read, change or delete your data.
Cross-site scripting
Attackers plant scripts that run in your users' browsers to steal sessions or send them somewhere else.
Bots and credential stuffing
Automated tools try stolen passwords at scale and hammer login pages, forms and APIs.
Unpatched vulnerabilities
When a flaw is found in an application, a firewall in front of it buys you time while a fix isn't ready yet.
Where it fits
One gateway in front of every application
NullWard sits between the internet and your applications. Every request passes through it first, so inspection, certificates, sign-in and logging happen in one place, on infrastructure you control, for as many domains and applications as you run.
The internet
- Customers and staff
- Partners and API clients
- Bots and scanners
- Attackers
Your gateway
NullWard
- OWASP Core Rule Set WAF
- Automatic TLS
- Sign-in for any app
- Threat intelligence
- Rate limiting
- Audit logging
Your applications
- Websites and customer portals
- APIs
- Internal tools and dashboards
- Apps in private networks, through tunnels
In practice
Built to be tuned, not just switched on
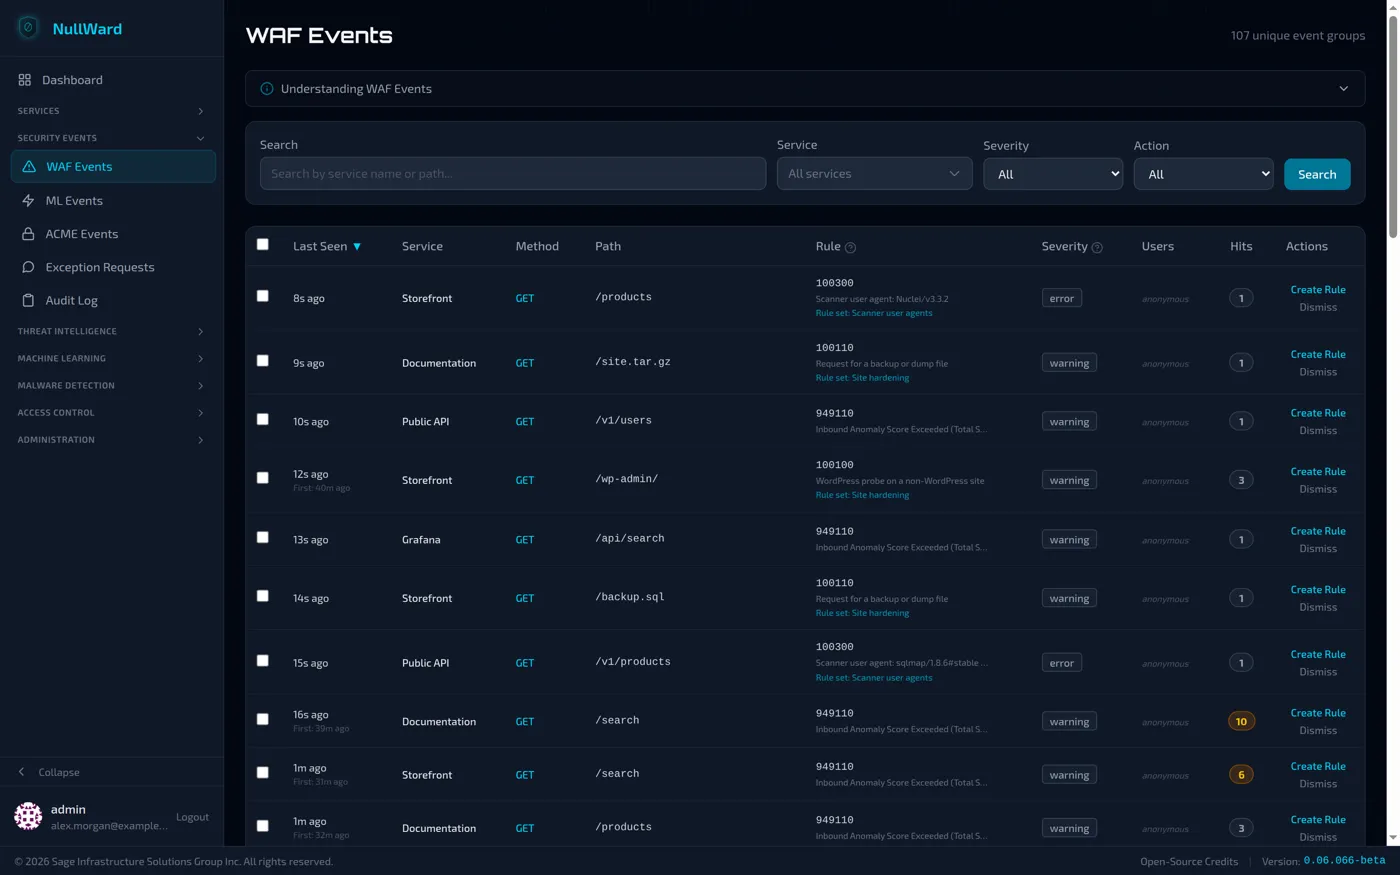
Stop attacks without blocking your users
The OWASP Core Rule Set v4 blocks common attacks out of the box. Run a new service in audit-only mode first, triage events grouped by rule, and turn a false positive into a precise exclusion in one click. Add your own SecLang rules globally or per service, with validation as you type.
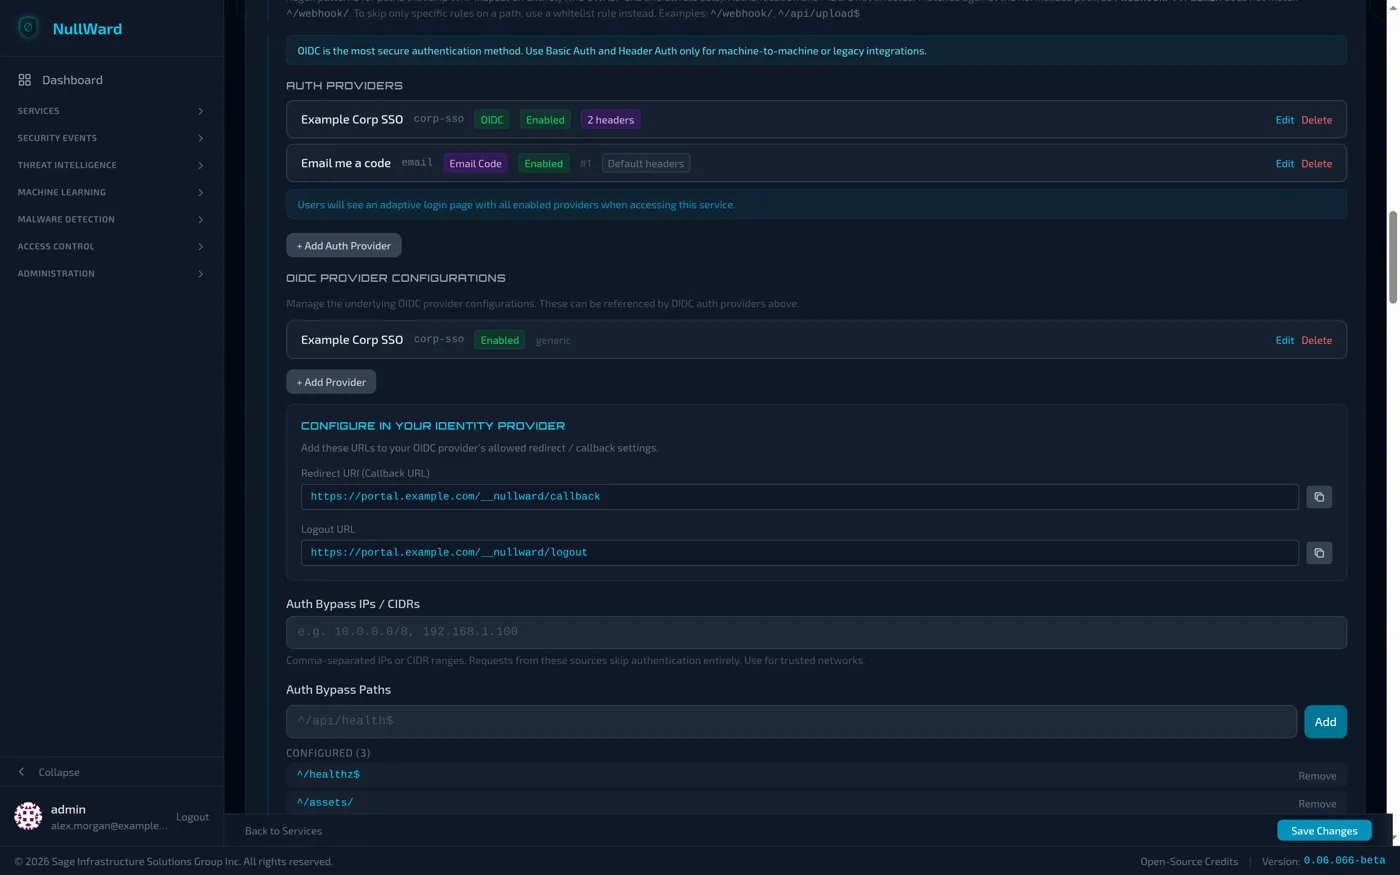
Sign-in for any application, with no code changes
Put OIDC single sign-on with Entra ID or Google, LDAP / Active Directory, or one-time email codes in front of any application, even ones with no login of their own, and pass the user's identity through to the app.
Application tunnels (licensed)
How application tunnels work
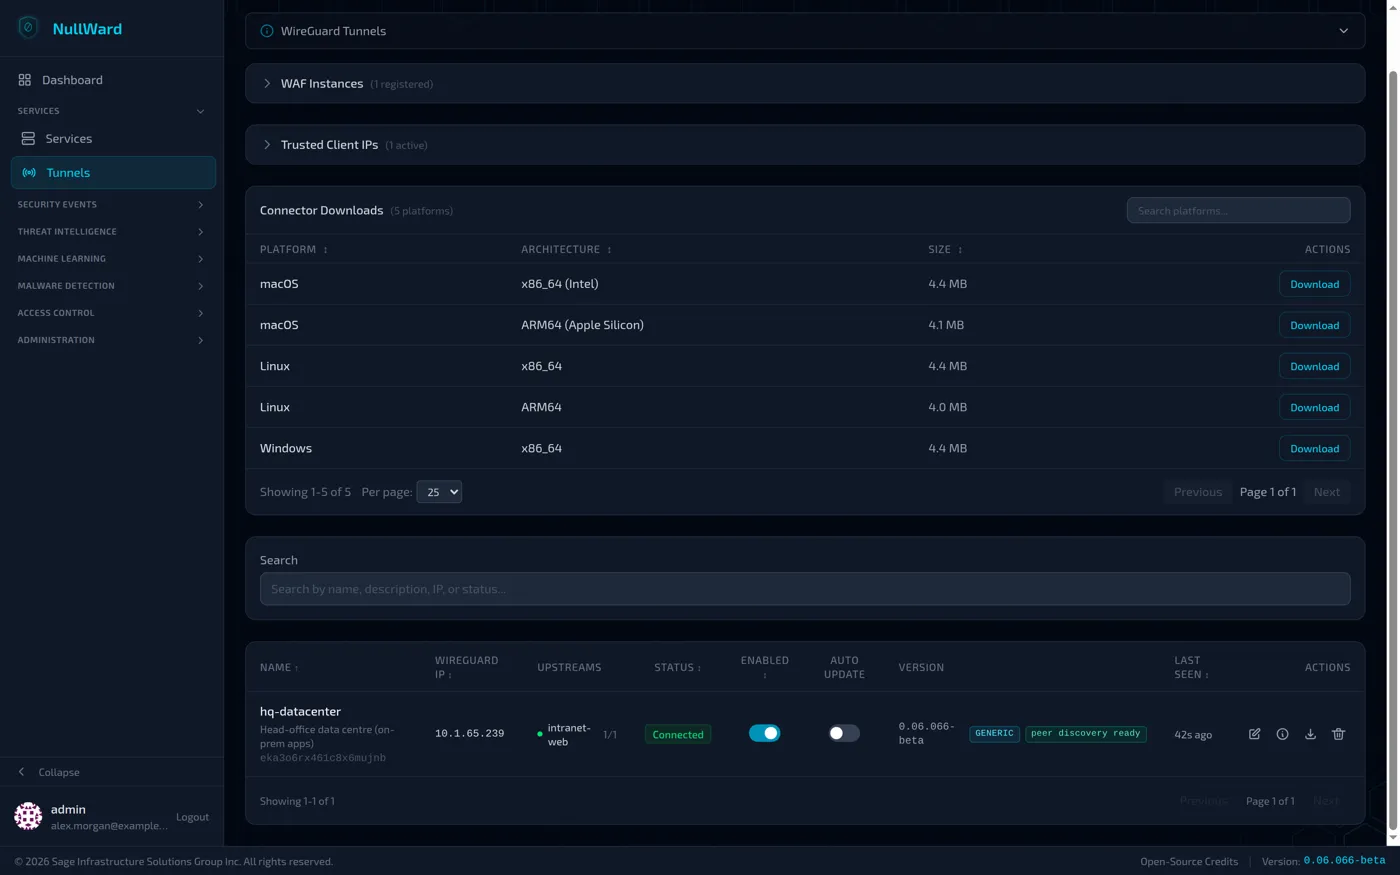
Application tunnels let you publish applications that live behind NAT, in a private network or in Kubernetes, without opening a single inbound port on your firewall.
Install the connector next to your app
Run the lightweight tunnel connector on the same network as your application. Downloads are available for five platforms, and a Kubernetes operator is included.
It connects outward to NullWard
The connector opens an encrypted WireGuard tunnel out to your NullWard gateway. Nothing has to reach into your network, so there are no inbound firewall rules to create.
Visitors arrive through NullWard
Requests reach your application through NullWard, so the WAF, sign-in and TLS protect every request before it travels down the tunnel.
Pricing
Free to use. Licensed when you need more.
NullWard is free for both commercial and personal use. Any license unlocks every paid feature, and you can try them all free for 30 days with no card needed.
Everything you need to protect your apps
- OWASP Core Rule Set WAF
- Custom rule sets
- Automatic TLS certificates
- Sign-in for any application
- Threat intelligence and auto-blocking
- Visibility and audit
- Unlimited domains and applications
Everything free, plus
- ML WAF
- Application tunnels
- Virtual waiting room
- High availability clustering (beta)
- HTTP/3 (beta)
- Priority email support on Professional and above
NullWard ships as container images and a Helm chart, and runs on infrastructure you control.